Enterprise security teams dread compliance audits not because cloud infrastructure is inherently insecure, but because manual evidence gathering across AWS, Azure, and GCP creates massive engineering toil.
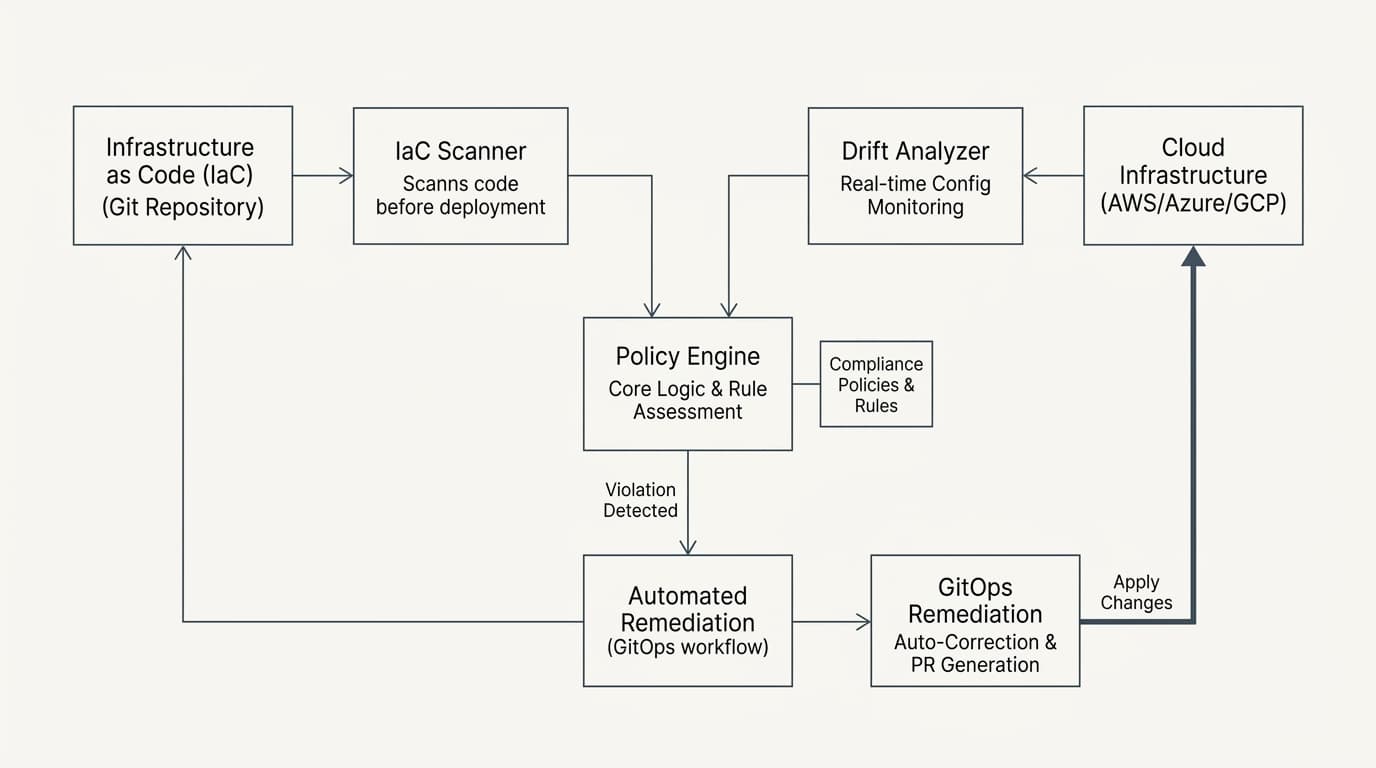
We built an autonomous compliance engine that parses Terraform and OpenTofu Abstract Syntax Trees (AST) in CI/CD, verifies configurations against SOC 2 Type II and HIPAA matrices, and generates verified GitOps remediation pull requests before misconfigurations reach production.
Static IaC AST scanning vs runtime reactive alerts
Traditional CSPM tools alert after a bucket is public or an unencrypted volume is provisioned. In an enterprise with hundreds of developers, runtime alerts produce severe alert fatigue and leave compliance windows exposed.
Our pipeline intercepts Terraform plans inside the CI/CD pull request cycle. By inspecting the HCL AST directly, the compliance engine identifies missing customer-managed KMS encryption, permissive CIDR ingress blocks, and wildcard IAM policies at the line-of-code level.
“Prevent compliance violations at pull request time rather than chasing drift in production.”
Automated drift detection & state healing
When emergency console changes cause configuration drift, the agent correlates AWS CloudTrail and Azure Monitor audit events. If benign, it generates an automated PR back into the repository to codify state. If non-compliant, it triggers an automated rollback plan with precise justification.
Auditing & production SLA metrics
| Dimension | Metric |
|---|---|
| Supported frameworks | SOC 2 Type II, HIPAA, ISO 27001, PCI-DSS v4 |
| Pre-deployment scan latency | < 4.2 seconds per Terraform plan |
| Audit preparation time | Reduced from 280 hours to 0 hours |
| Remediation mechanism | Automated PR with syntactically valid HCL diffs |
| Multi-cloud coverage | AWS, Azure, and Google Cloud Platform |
Key architectural takeaways for CTOs
Shifting compliance left into the AST parser turns security from an adversarial audit gatekeeper into an automated developer accelerator with zero manual evidence collation.
Engineering Principle in Production
How multi-cloud IaC AST parsing, automated IAM drift detection, and continuous GitOps remediation PRs cut audit preparation from 8 weeks to zero manual overhead.
